
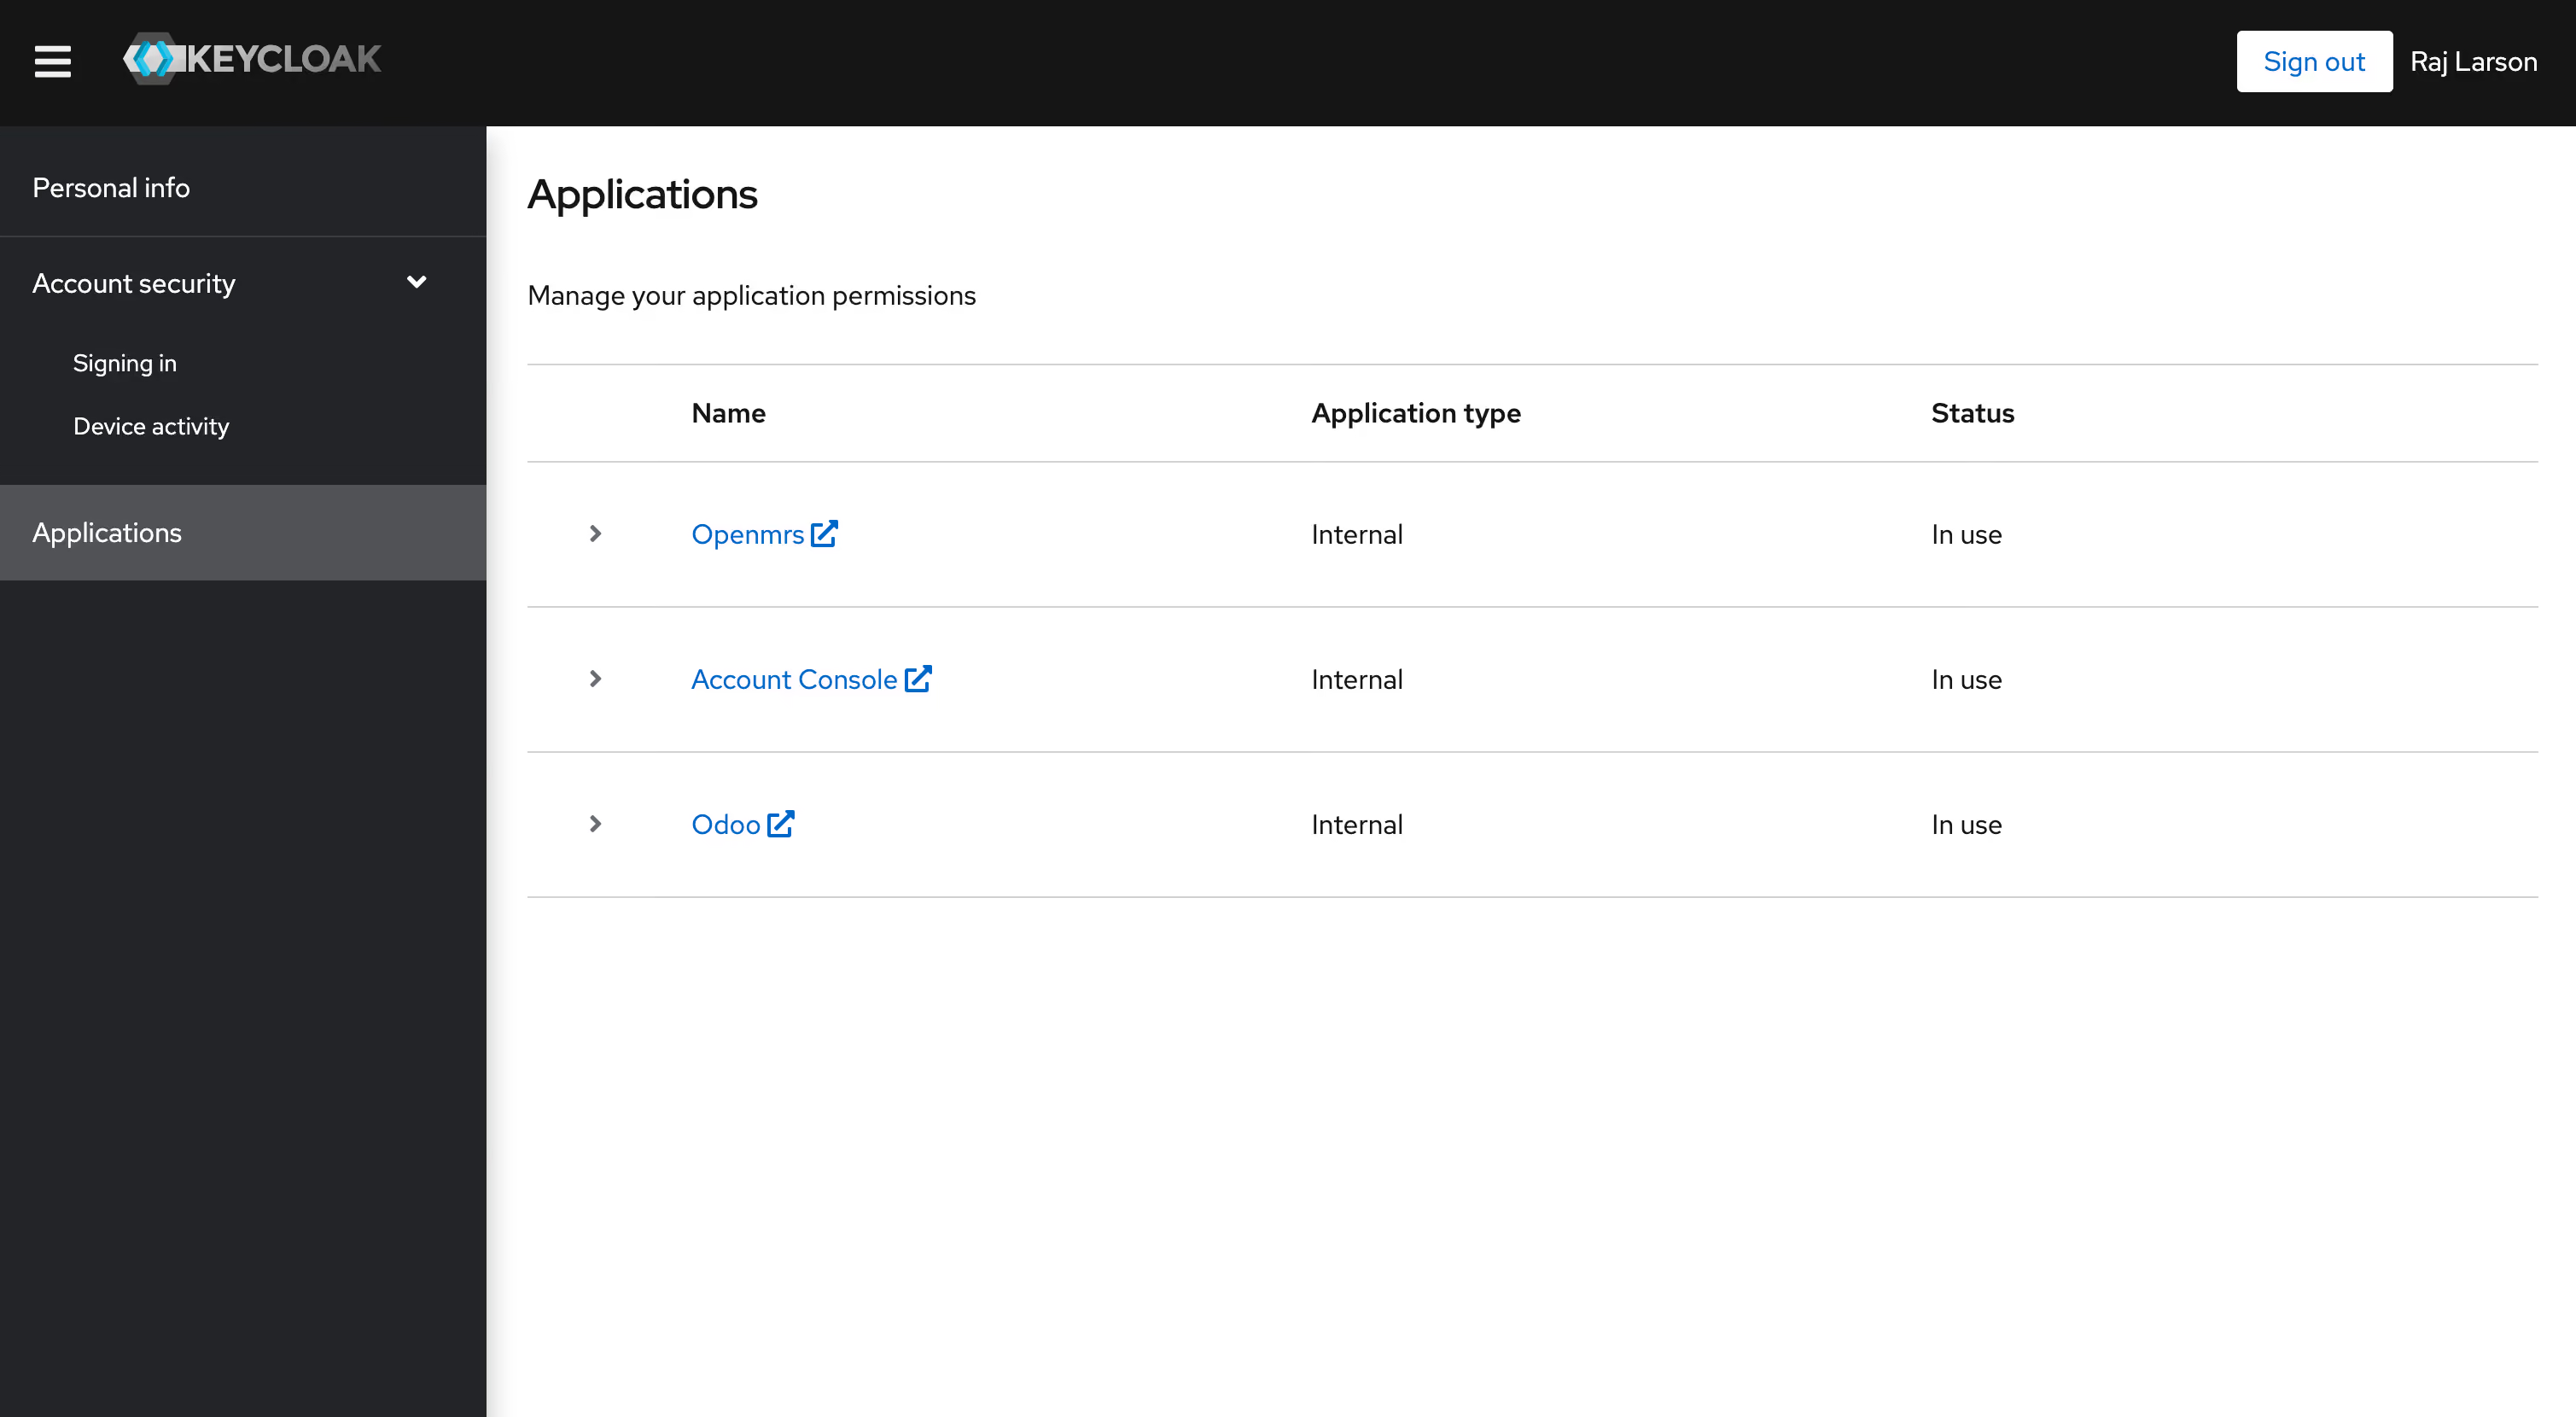
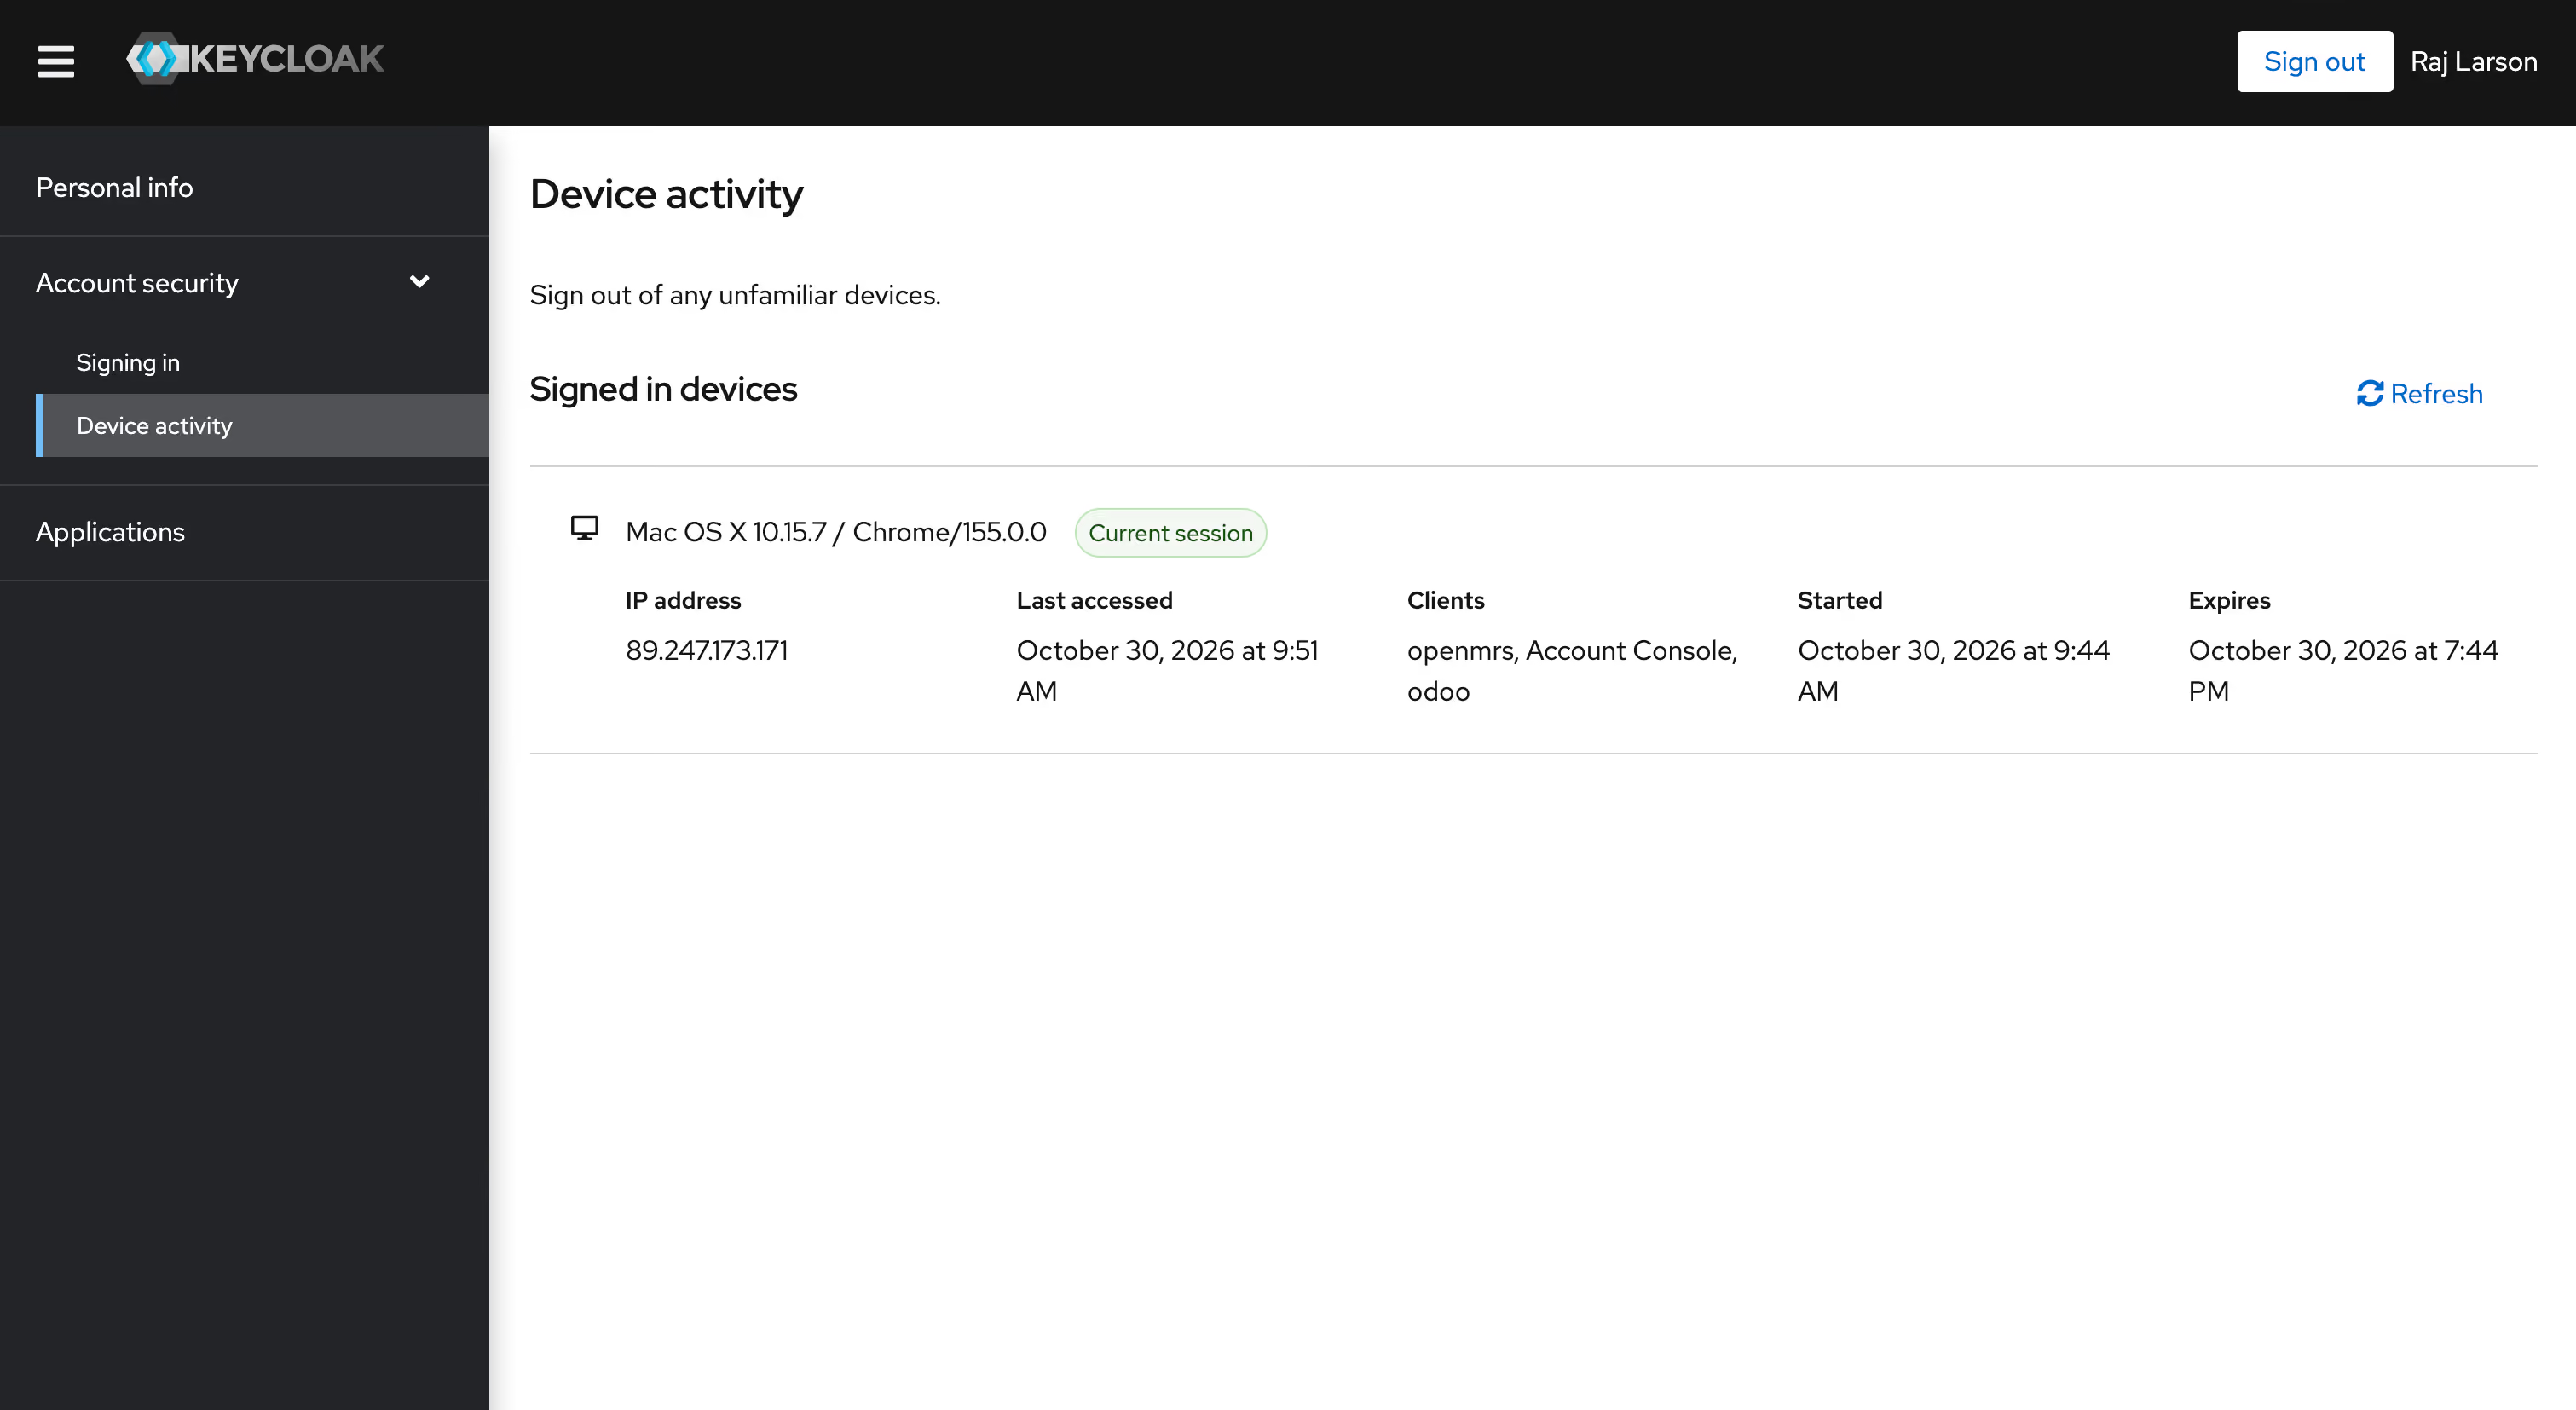
Keycloak
An open-source identity and access management solution that provides SSO capabilities to Ozone HIS. Keycloak supports standard protocols such as OpenID Connect, OAuth 2.0, and SAML 2.0.
- Single sign-on across all Ozone apps: one login for the EMR, ERP, lab and analytics
- Central user, group and role management
- Roles defined once in Keycloak and applied in connected apps (e.g. Odoo, Superset)
- Standard protocols: OpenID Connect, OAuth 2.0 and SAML 2.0
- Multi-factor authentication (OTP, WebAuthn/passkeys) and password policies
- Identity brokering with external providers (Google, Microsoft Entra ID, other OIDC/SAML IdPs)
- User federation with LDAP and Active Directory
- Customisable login pages, themes and self-service account console
- Audit events and session management, including single sign-out
Keycloak was created at Red Hat, which remains a major contributor and ships a supported build as Red Hat build of Keycloak. Since 2023 it has been an incubating project of the Cloud Native Computing Foundation (CNCF), governed openly with maintainers from several companies. It is released under the Apache 2.0 licence with regular major releases.
- SSO is optional in Ozone and switched on with the
ENABLE_SSOsetting; without it, each app keeps its own login. - Each Ozone app is registered as a client in the Ozone realm; adding a new app means adding a client, redirect URIs and web origins.
- Ozone's realm configuration loads with an "ignore existing" strategy, so changes made in the admin console are not overwritten on restart, but config changes in files are not applied to an existing realm either.
- User claims include attributes such as gender and provider, used to link a Keycloak user to an OpenMRS provider.
- Keycloak needs its own database (PostgreSQL in Ozone's default stack); back it up with the other app databases.
- Run it behind HTTPS with a stable public hostname; changing the hostname later breaks client redirects and issued tokens.
- Keep the admin console off the public internet and enforce MFA for administrators.